Practice & Projects
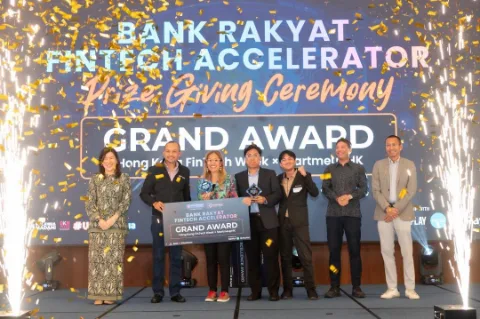
AI Fraud Detection: T-NEX Wins Bank Rakyat Award
T-NEX wins Bank Rakyat’s Grand Award with two finalists: AI fraud detection and credit assessment with CCPT scoring. Insights for banking teams.
Analyses and practice-oriented articles by the T-NEX editorial team: regulation, AI and governance, technology and operations, practice and projects. The articles identify their sources and the date of the current revision. T-NEX GmbH is the publisher.
32 articles
Practice & Projects
T-NEX wins Bank Rakyat’s Grand Award with two finalists: AI fraud detection and credit assessment with CCPT scoring. Insights for banking teams.
Regulation
The DORA register of information: record contracts, identifiers and supply chains using the EU templates and BaFin requirements.
Technology & Operations
Compare 682 GRC providers worldwide: specific AI functions, vendor sources and specialist areas. With detailed profiles and a Europe selection.
Technology & Operations
379 GRC providers in Europe, 320 of them with documented AI. Countries, specialist areas and review questions for banks and regulated companies.
Practice & Projects
Allocate and manage IT costs in banks: budget, forecast and cost allocation in a fully worked calculation case. With AI review questions and free worksheets.
Technology & Operations
How banks support compliance tasks with AI and workflows: requirements, gap analysis, approvals and evidence. With a continuous sample case.
Regulation
Assessing and managing changes at ICT service providers: a DORA practical case for banks with an evidence matrix, decision template and Banking Platform reference.
Regulation
NIS2 and DORA for banks: compare scope, BSI registration, reporting deadlines and ICT providers, with references to Germany’s BSIG.
AI & Governance
How RAG chatbots retrieve documents and support answers, with checks for permissions, knowledge maintenance and answer quality.
AI & Governance
AI agents in financial institutions: limit tasks and permissions, assess approvals and trace actions under MaRisk, DORA and the AI Act.
AI & Governance
The AI Act for banks after the July 2026 amendment: high-risk classification, transparency and current application dates.
Regulation
AMLR from 10 July 2027, staged AMLD6 implementation and AMLA supervision: responsibilities and dates financial institutions need to assess.
Technology & Operations
Assess GRC software through functions, contractual requirements and operating evidence under MaRisk and DORA.
Regulation
Key banking dates for DORA, MaRisk, AI regulation and anti-money laundering, with sources distinguishing applicable law from plans.
Regulation
The ninth MaRisk amendment has applied since 30 June 2026. Changes from the previous version and implementation checks for institutions.
Regulation
MaRisk under Circular 06/2026: scope, structure and relationship with DORA, including the limited transition and investment-firm distinction.
Regulation
DORA since 17 January 2025: scope, ICT risk, incident reporting and third parties, with primary sources and implementation checks.
Regulation
ICAAP and ILAAP for banks in Germany: normative and economic perspectives, a worked example, SREP and the ECB's July 2026 clarifications.
Regulation
Understand P2R and P2G, CET1 composition and MDA. A worked capital example and 2026 methodology changes for ECB banks and German LSIs.
Regulation
Classify outsourcing and ICT services under MaRisk AT 9 and DORA Articles 28–30. Contracts, registers, risk assessments and practical exit testing.
Regulation
CRR III since 2025: the output floor rises from 55% in 2026 to 72.5% from 2030. Worked calculation and FRTB transitional measures for 2027–2029.
Regulation
IReF for banks: planned pilot from Q2 2030 and official reporting from Q2 2031. How BIRD, AnaCredit and supervisory reporting differ, and how to prepare data.
Regulation
A curated map connects guideline identifiers, business topics and German supervisory practice. It starts with the implementation list in MaRisk of 30 June 2026.
Regulation
A GRC migration starts with fields, responsibilities and data quality. This sequence moves from the existing workbook through a trial run to business acceptance.
Regulation
TLPT is advanced testing for financial entities identified by the supervisor. Selection follows DORA and Commission Delegated Regulation (EU) 2025/1190.
Regulation
The SREP connects business model, governance, capital risks and liquidity risks. Banks need a consistent account of their data, assumptions, decisions and outstanding actions.
Regulation
COREP principally addresses prudential risks and own funds. FINREP provides standardised financial information. Reliable reporting requires aligned definitions, sources and reconciliations.
Regulation
A sound business case compares current operations with specific alternatives. It shows implementation effort, recurring cost and evidenced benefits over the same period.
Regulation
Solvency II combines quantitative capital requirements with governance and reporting. This overview explains SCR, MCR and the role of ORSA in managing an insurer.
Regulation
Sanctions screening requires current legal and list data, appropriate matching and traceable alert handling. A similar name starts an investigation.
Regulation
ISO/IEC 27001 defines requirements for an information security management system. IT-Grundschutz adds a concrete methodology and building blocks. Begin with scope and the evidence you need.
Regulation
Bank data has no single retention period. A deletion policy connects record type, legal basis, start date and justified exceptions with the data actually held.
Regulation here means DORA, MaRisk, BAIT and European supervisory practice, explained from primary sources. Every article names the legal act, the article and the exact reference, so each statement remains verifiable and can be carried straight into your own implementation.
AI and governance covers the use of language models in banks: control frameworks, traceability, source binding and the question of when an AI answer holds up in an audit. The benchmark is supervisory expectation, not what is technically possible.
Technology and operations shows how AI systems actually run in banking environments: architecture, hosting in the EU, operating models and outsourcing questions, described concretely enough that IT, business and internal audit speak the same language.
Practice articles explain individual steps and decisions from documented projects. Measurements are identified with the test or operating conditions they describe.